Friday, 8 July 2011


Wednesday, 15 June 2011
Guys Is your Nokia Cell Phone Original or not???????

Press the following on your mobile *#06# to see your Phone�s IMEI number(serial number).
Then check the 7th and 8th numbers.
Phone serial no. x x x x x x ? ? x x x x x x x
IF the Seventh & Eighth digits of your cell phone are 02 or 20 this means your cell phone was assembled in Emirates which is very Bad quality.
IF the Seventh & Eighth digits of your cell phone are 08 or 80 this means your cell phone was manufactured in
IF the Seventh & Eighth digits of your cell phone are 01 or 10 this means your cell phone was manufactured in
IF the Seventh & Eighth digits of your cell phone are 00 this means your cell phone was manufactured in original factory which is the best Mobile Quality.
IF the Seventh & Eighth digits of your cell phone are 13 this means your cell phone was assembled in Azerbaijan which is very Bad quality and also dangerous for your health.
Posted By: Anshuman Kak
Tuesday, 17 May 2011
How to find a vulnerable Website?

"Betting Your Website is Safe From Hackers?That's a Bet over 8 out of 10 Will Lose!"
Website security is a major problem today and should be a priority in any organization or a webmaster, Now a days Hackers are concentrating alot of their efforts to find holes in a web application, If you are a website owner and having a High Page rank and High Traffic then there is a chance that you might be a victim of these Hackers.
Few years back their existed no proper tools search for vulnerability, but now a days there are tons of tools available through which even a newbie can find a vulnerable site and start Hacking
Methods used for Website Hacking
There are lots of methods that can be used to hack a website but most common ones are as follows:
1.SQL Injection
2.XSS(Cross Site Scripting)
3.Remote File Inclusion(RFI)
5.Local File inclusion(LFI)
6.DDOS attack
Acunetix
Acunetix is one of my favorite tool to find a venerability in any web application It automatically checks your web applications for SQL Injection, XSS & other web vulnerabilities.

Nessus
Nessus is the best unix venerability testing tool and among the best to run on windows. Key features of this software include Remote and local file securitychecks a client/server architecture with a GTK graphical interface etc.
Download Nessus from the link below
Retina-
Retina is another Vulnerability assessment tool,It scans all the hosts on a network and report on any vulnerabilities found.
Download Retina from the link below
Metasploit Framework:
The Metasploit Framework is the open source penetration testing framework with the world's largest database of public and tested exploits.
Download Metasploit(For Windows users) from the link below
Download Metaspolit(For Linux users) from the link below
Regards : Anshuman Kak a Script kiddie
Saturday, 30 April 2011
Gathering Wordpress Version Of A Website/Blog

To Hack a Wordpress Website/Blog Hacker tries to find out the version number of that CMS (Content managing System). A Content Management System (CMS) is a computer program that allows publishing, editing and modifying the content as well as maintenance from a central interface. Such systems of content management provide procedures to manage workflow in a collaborative environment So he could go and search on Exploit databases for possible exploits.
For example: Take http://ethicalhacking1.com/blog
In a Wordpress blog Hacker can easily find out some one's version number by just viewing the source of that particular blog.
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd">
<html xmlns="http://www.w3.org/1999/xhtml">
<head profile="http://gmpg.org/xfn/11">
<meta http-equiv="Content-Type" content="text/html; charset=UTF-8" />
<title>Ethical Hacking, Network Security, Cyber Security with Sahil Baghla</title>
<meta name="generator" content="********" /> <!-- Leave this for stats -->
<script type="text/javascript">
/***********************************************
Now it's not a good idea to expose your version number because it will make your Website/blog more vulnerable to hackers.
There are a couple of ways through which you can hide your version numbers, The simplest one is to add the following code inside your functions.php file
remove_action('wp_head', 'wp_generator');
Moreover there are a couple of other plugins which can help you hide your Wordpress plugin, Just google for them.
Well even if anyone is using plugins to hide their Wordpress version number,
it is still possible for a hacker to determine your version number, All the hacker has to do is to add "/readme.html" after the websites URL.
it is still possible for a hacker to determine your version number, All the hacker has to do is to add "/readme.html" after the websites URL.
Countermeasures:
1. Use a good plugin that can hide your Wordpress version number.
2. Always update your Wordpress to the latest version.
3. Either delete readme.html file or change it to something like readme.php file.
NOTE::The Text Highlighted in Red is The version Of the blog..
Posted By: Anshuman Kak
Saturday, 23 April 2011
Best Network Security Scanners
What are scanners?
Scanners, the subject of this post, are "neutral" network applications. this means that they can help both a hacker and an administrator. Their task is to collect information about network devices. As it turns out, this information can be quite varied. We are able to discover which software is used in the system, to check how long it has been running, and to find out about the available ports. Of course the scanners are written in such a way that their activity won't leave unwanted footprints on the target machine. It happens often that scanning is performed using undocumented protocols, the monitoring of which is usually ignored.
The advantages this presents may seem to be useful only to a hacker, but they are also important to an administrator. They allow us to make appropriate changes to the settings and improve the system security level.
There are three popular scanners, Nmap, Nessus, and Nikto. Each of these applications provides different functions, and they complement each other perfectly.
NMAP

Nmap (Network Mapper) is a security scanner originally written by Gordon Lyon (also known by his pseudonym Fyodor Vaskovich) used to discover hosts and services on a computer network, thus creating a "map" of the network. To accomplish its goal, Nmap sends specially crafted packets to the target host and then analyzes the responses. Unlike many simple port scanners that just send packets at some predefined constant rate, nmap accounts for the network conditions (latency fluctuations, network congestion, the target interference with the scan) during the run. Also, owing to the large and active user community providing feedback on its features and contributing back, nmap has succeeded to extend its discovery capabilities beyond basic host being up/down or port being open/closed to being able to determine operating system of the target, names and versions of the listening services, estimate uptime, the type of device, presence of the firewall. [from Wikipedia]
Nmap runs on Linux, Microsoft Windows, Solaris, HP-UX and BSD variants (including Mac OS X), and also on AmigaOS and SGI IRIX. Linux is the most popular nmap platform with Windows following it closely.
Nessus

Nessus is an application that is worth to discuss about. This program is similar in funcionality to nmap, but it distinguishers itself by an extended error detabase, updated every day, that is very useful for the user. In addition, Nessus is easy to keep up to date, using a plugin system for this purpose. The plugins are created with a special NASL script language. Information about the application can be obtained on the homepage of the project: http://www.nessus.org/
Nikto

Nikto performs comprehensive tests against web servers for multiple items, including over 6100 potentially dangerous files/CGIs, versions on over 950 servers, and version specific problems on over 260 servers.
Regards: Anshuman kak a Script kiddie
Tuesday, 19 April 2011
�GET A FREE facebook T-SHIRT� � New Facebook Scam!

Guys If you come across any Post on facebook that says �GET A FREE facebook T-SHIRT�, please Ignore it. This is not a likejacking type of SPAM, but the Pure and Simple social engineering example to Capture user data. The Scammers have created a n external web page, whose look and feel closely matches with facebook�s user interface.
Though looking at that page you can easily make out that its a scam, Still Some people will get tempted and will Register their email and home address there.
Lets see how these scammers are cheating you in the name of �free Facebook T-shirt�. First they are asking you to complete some Steps to be able to receive your T-shirt.

As you can see above they are first asking you to Share their Page on your wall, so that your friends can also register for the same. In the Next step, you will be asked to join their group, so that they can repeatedly spam you Facebook Inbox with their offers.

Next they will ask you to Like your Country .. and as you can see large no. of Indians have already tried this �Unbelievable!!!
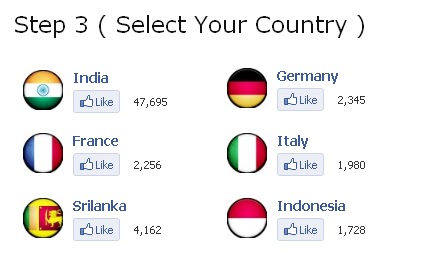
And then Finally They will ask you to Register For their Free T-shirt. This is what the main aim of scammers is. They just collected your Personal details and Now they can use it to register any website or Spam your email account with their Scam offers. Lets be aware of it and Do share this Information on Facebook to warn your friends too.

Saturday, 16 April 2011
Top 20 Hacking Tools

These are Top 20 Hacking Tools, the list is exhaustive, these are a few to name:
The �Nessus� Project aims to provide to the internet community a free, powerful, up-to-date and easy to use remote security scanner for Linux, BSD, Solaris, and other flavors of Unix.
Ethereal is a free network protocol analyzer for Unix and Windows. Ethereal has several powerful features, including a rich display filter language and the ability to view the reconstructed stream of a TCP session.
Snort is an open source network intrusion detection system, capable of performing real-time traffic analysis and packet logging on IP networks.
Netcat has been dubbed the network swiss army knife. It is a simple Unix utility which reads and writes data across network connections, using TCP or UDP protocol
TCPdump is the most used network sniffer/analyzer for UNIX. TCPTrace analyzes the dump file format generated by TCPdump and other applications.
Hping is a command-line oriented TCP/IP packet assembler/analyzer, kind of like the �ping� program (but with a lot of extensions).
DNSiff is a collection of tools for network auditing and penetration testing. dsniff, filesnarf, mailsnarf, msgsnarf, urlsnarf, and webspy passively monitor a network for interesting data (passwords, e-mail, files, etc.).
GFI LANguard Network Security Scanner (N.S.S.) automatically scans your entire network, IP by IP, and plays the devil�s advocate alerting you to security vulnerabilities.
>Ettercap is a multipurpose sniffer/interceptor/logger for switched LAN. It supports active and passive dissection of many protocols (even ciphered ones)and includes many feature for network and host analysis.
Nikto is an Open Source (GPL) web server scanner which performs comprehensive tests against web servers for multiple items, including over 2500 potentially dangerous files/CGIs, versions on over 375 servers, and version specific problems on over 230 servers.
John the Ripper is a fast password cracker, currently available for many flavors of Unix.
OpenSSH is a FREE version of the SSH protocol suite of network connectivity tools, which encrypts all traffic (including passwords) to effectively eliminate eavesdropping, connection hijacking, and other network-level attacks.
Tripwire is a tool that can be used for data and program integrity assurance.
Kismet is an 802.11 wireless network sniffer � this is different from a normal network sniffer (such as Ethereal or tcpdump) because it separates and identifies different wireless networks in the area.
NetFilter and iptables are the framework inside the Linux 2.4.x kernel which enables packet filtering, network address translation (NAT) and other packetmangling.
IP Filter is a software package that can be used to provide network address translation (NAT) or firewall services.
OpenBSD Packet Filter
fport identifys all open TCP/IP and UDP ports and maps them to the owning application.
SAINT network vulnerability assessment scanner detects vulnerabilities in your network�s security before they can be exploited.
OpenPGP is a non-proprietary protocol for encrypting email using public key cryptography. It is based on PGP as originally developed by Phil Zimmermann.
Posted by: Anshuman Kak
Subscribe to:
Posts (Atom)